دروازه اختیار برای ایجنتها: از سیگنال تا اقدامِ مجاز
ایجنت میتواند سیگنال را تشخیص دهد و اقدام پیشنهاد کند، اما نباید درباره توقف، اجرای ابزار یا ایجاد تعهد عملیاتی تصمیم نهایی بگیرد. یک دروازه سیاستی مستقل باید سطح اقدام، مالک، آستانه و مجوز را تعیین کند.
فهرست مطالب
ایجنتی که یک عدد غیرعادی میبیند، نباید صرفاً با اتکا به همان عدد بتواند workflow را متوقف کند، برای مدیران جلسه بسازد یا ابزار عملیاتی را فعال کند. عدد، حتی اگر درست محاسبه شده باشد، فقط یک سیگنال است. تبدیل سیگنال به اقدام، یک تصمیم اجرایی است و باید خارج از استدلال زبانی ایجنت کنترل شود.
مسئله اصلی در طراحی ایجنت، توانایی تولید پاسخ یا اتصال به ابزار نیست؛ مسئله، طراحی مرز اختیار است. ایجنت میتواند داده را گردآوری کند، شواهد را خلاصه کند، ناهنجاری را تشخیص دهد و اقدام پیشنهاد کند. اما نباید خودش تعیین کند که پیشنهادش اطلاعرسانی است، کار ایجاد میکند، به تأیید نیاز دارد یا مجاز به اجراست.
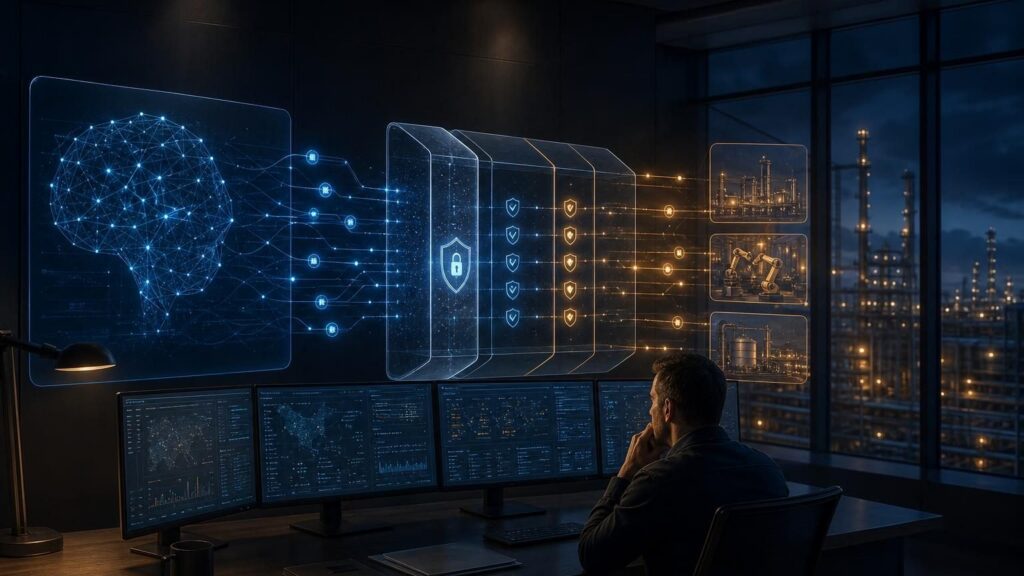
الگوی مناسب، قرار دادن یک دروازه مجوزدهی میان ایجنت و اجرای workflow است. ایجنت درخواست اقدام تولید میکند؛ دروازه سیاستی آن درخواست را با قواعد قطعی ارزیابی میکند؛ و فقط یک مجری محدودشده، در صورت وجود مجوز معتبر، ابزار عملیاتی را فراخوانی میکند.
این دروازه باید با policy-as-code کار کند. یعنی قواعد تصمیم بهصورت ساختیافته، نسخهپذیر، قابلآزمون و قابلممیزی تعریف شوند. قاعده نباید به برداشت آزاد از یک prompt، توضیح متنی ایجنت یا قضاوت لحظهای یک مدل زبانی وابسته باشد.
درخواست اقدام ایجنت باید ساختار مشخصی داشته باشد. حداقل اجزای آن شامل نوع سیگنال، شناسه پرونده، شواهد، منبع داده، زمان تولید داده، دامنه اثر، مالک فرایند، اقدام پیشنهادی و سطح ریسک پیشنهادی است. سطح ریسک میتواند از سوی ایجنت پیشنهاد شود، اما نباید حکم نهایی تلقی شود.
دروازه سیاستی باید خروجی خود را به چند وضعیت محدود و روشن تبدیل کند: no-op برای ثبت بدون اقدام، notify برای اطلاعرسانی، create-task برای ایجاد کار قابلپیگیری، require-approval برای توقف پیش از اجرا و allow برای اجرای خودکار. هر وضعیت باید معنای عملیاتی مشخص، مالک مشخص و مسیر اجرایی مشخص داشته باشد.
تفکیک تشخیص از مجوز، خطای مدل را از اختیار عملیاتی جدا میکند. مدل ممکن است متن را نادرست تفسیر کند، یک رویداد را اشتباه طبقهبندی کند یا شواهد ناکافی را بیش از حد قانعکننده نشان دهد. اما اگر دروازه سیاستی مستقل باشد، چنین خطایی نباید بهتنهایی ابزار حساس را فعال کند.
برای مثال فرضی، یک ایجنت کیفیت ممکن است تشخیص دهد که نرخ رد در یک دسته تولید از آستانه مشاهده عبور کرده و توقف ارسال را پیشنهاد دهد. دروازه نباید فقط به عبارت «توقف ارسال» یا امتیاز ریسک ایجنت واکنش نشان دهد. باید بررسی کند که داده از منبع مجاز آمده یا نه، تازه است یا نه، دسته موردنظر چیست، مالک تصمیم چه کسی است و آیا توقف خودکار در آن دامنه از پیش مجاز شده است یا نه.
آستانه بهتنهایی تصمیم نمیسازد. هر آستانه باید به تعریف شاخص، دوره سنجش، کیفیت داده، تازگی داده، دامنه محصول یا فرایند، شدت پیامد و مالک پاسخگو متصل باشد. عددی که از نظر آماری برجسته است، لزوماً حق ایجاد اختلال عملیاتی ندارد.
قواعد باید از زبان مبهم فاصله بگیرند. بهجای نوشتن «اگر ریسک بالا بود، مدیر را در جریان بگذارید»، باید مشخص شود کدام متغیرها ریسک را تعیین میکنند، کدام نقش اطلاع دریافت میکند، چه زمانی کار ایجاد میشود، چه کسی مجاز به تأیید است و پس از کدام تصمیم، کدام ابزار قابل فراخوانی خواهد بود.
هر قاعده حداقل به شرط ورود، دامنه اعتبار، اولویت، خروجی مجاز، مالک تصمیم، زمان انقضا و الزام ثبت ممیزی نیاز دارد. دامنه اعتبار مشخص میکند که قاعده برای کدام واحد، فرایند، نوع داده یا سطح پیامد قابل استفاده است. زمان انقضا نیز مانع استفاده از مجوزها یا قواعدی میشود که دیگر با وضعیت عملیاتی سازگار نیستند.
تعارض قواعد باید از پیش طراحی شود، نه اینکه هنگام اجرا به مدل واگذار شود. قاعده پایه میتواند این باشد که خروجی محدودکنندهتر مقدم است: deny یا no-op بر allow مقدم میشود و require-approval بر اجرای خودکار ارجحیت دارد. اگر تعارض با این ترتیب حل نشود، خروجی پیشفرض باید require-approval باشد و دلیل تعارض در رسید تصمیم ثبت شود.
رفتار fail-safe نیز باید صریح باشد. اگر دروازه سیاستی در دسترس نیست، منبع داده قابل اعتبارسنجی نیست، ثبت ممیزی انجام نمیشود یا وضعیت تأیید قابل بررسی نیست، اجرای ابزارهای حساس نباید مجاز باشد. در چنین وضعیتی، سیستم میتواند no-op برگرداند یا create-task و notify را برای بررسی انسانی ایجاد کند، اما نباید allow صادر کند.
این اصل باید برای داده ناقص نیز برقرار باشد. نبود شناسه پرونده، نامشخص بودن مالک، قدیمی بودن داده، تکراری بودن درخواست یا ناکافی بودن شواهد، دلیل مناسبی برای اجرای سریع نیست. دروازه باید درخواست را رد کند، برای تکمیل اطلاعات کار بسازد یا آن را به مسیر تأیید انسانی بفرستد.
notify و create-task دو خروجی متفاوتاند. notify فقط آگاهی ایجاد میکند و تعهد اجرایی تازهای به وجود نمیآورد. create-task باید مالک، موعد، وضعیت و انتظار خروجی داشته باشد. مخلوط کردن این دو، یا سازمان را با هشدارهای بیاثر مواجه میکند یا از هر سیگنال کماهمیت یک صف کار میسازد.
require-approval نیز نباید صرفاً یک دکمه تأیید باشد. درخواست تأیید باید نشان دهد چه اقدامی قرار است انجام شود، بر پایه کدام شواهد، در چه دامنهای، با چه پیامد و تا چه زمانی معتبر است. تأییدکننده باید بتواند اقدام را بپذیرد، رد کند، دامنه آن را محدود کند یا درخواست را برای شواهد بیشتر بازگرداند.
allow فقط برای اقداماتی مناسب است که دامنه اثر محدودی دارند، برگشتپذیرند یا مسیر بازگشت روشن دارند و تحت قاعدهای پایدار و آزموده قرار گرفتهاند. شباهت ظاهری دو درخواست نباید مجوز یکسان ایجاد کند. تغییر در منبع داده، دامنه اثر، نوع ابزار یا پیامد اقدام باید ارزیابی مجوز را دوباره فعال کند.
ثبت تصمیم بخشی از کنترل است، نه یک کار اداری اضافی. هر رویداد باید نشان دهد چه ورودیهایی دریافت شد، کدام نسخه سیاست اعمال شد، کدام قواعد منطبق بودند، چه تعارضی رخ داد، چه خروجی صادر شد، چه کسی تأیید کرد و اجرای نهایی چه نتیجهای داشت. بدون این رسید، اصلاح قواعد و بررسی خطاها به حدس وابسته میشود.
ارزیابی این معماری نباید فقط بر کیفیت پاسخ ایجنت متمرکز باشد. باید سناریوهای مرزی مانند داده ناقص، قواعد متعارض، درخواست تکراری، تأیید منقضی، تغییر مالک، ابزار در دسترسنبودن و اقدام نیمهانجامشده نیز آزموده شوند. معیار مهم این است که سیستم در ابهام به حالت امنتر برود، نه اینکه صرفاً پاسخ روانتری تولید کند.
برای شروع، لازم نیست همه فرایندها را وارد دروازه سیاستی کنید. یک تصمیم پرتکرار با پیامد مشخص انتخاب کنید؛ اقدامهای ممکن را به پنج خروجی محدود کنید؛ برای هر خروجی مالک، آستانه و زمان انقضا تعیین کنید؛ و موارد نیازمند تأیید را از موارد قابلاجرا جدا سازید. سپس بر اساس رسیدهای تصمیم، قواعد را اصلاح کنید، نه اینکه اختیار ایجنت را با prompt بزرگتر گسترش دهید.
بلوغ در استفاده از ایجنت یعنی سازمان دقیقاً بداند کدام سیگنال، تحت چه شرایطی، به کدام اقدام تبدیل میشود و چه کسی مسئول آن است. در این مدل، ایجنت سرعت مشاهده و آمادهسازی تصمیم را بالا میبرد؛ اما سیاست مستقل، مرز اختیار را تعیین میکند. این جداسازی، AI را از یک محرک غیرقابلپیشبینی به بخشی کنترلپذیر از عملیات تبدیل میکند.
An agent that detects an unusual number should not be able to stop a workflow, schedule meetings for managers, or activate an operational tool on the strength of that number alone. A metric, even when calculated correctly, is only a signal. Turning a signal into action is an execution decision and should be controlled outside the agent’s language-based reasoning.
The central issue in agent design is not answer generation or tool connectivity; it is the design of authority boundaries. An agent can gather data, summarize evidence, detect anomalies, and propose an action. It should not decide on its own whether that proposal is a notification, creates a task, requires approval, or is permitted to execute.
The appropriate pattern is to place an authorization gateway between the agent and workflow execution. The agent produces an action request; the policy gateway evaluates that request against deterministic rules; and only a constrained executor invokes an operational tool when valid authorization exists.
This gateway should operate through policy-as-code. That means decision rules are defined in structured, versioned, testable, and auditable form. A rule should not depend on open-ended interpretation of a prompt, an agent’s textual explanation, or the momentary judgment of a language model.
The agent’s action request should have a defined structure. At minimum, it should include the signal type, case identifier, evidence, data source, data creation time, impact scope, process owner, proposed action, and proposed risk level. The agent may suggest a risk level, but it must not be treated as the final judgment.
The policy gateway should reduce its decision to a limited set of clear states: no-op for recording without action, notify for delivering information, create-task for creating trackable work, require-approval for stopping before execution, and allow for automatic execution. Each state should have a defined operational meaning, a defined owner, and a defined execution path.
Separating detection from authorization separates model error from operational authority. A model may misinterpret text, classify an event incorrectly, or present insufficient evidence as overly persuasive. But if the policy gateway is independent, such an error should not by itself activate a sensitive tool.
In a hypothetical example, a quality agent may detect that a rejection rate in a production batch has crossed an observation threshold and propose stopping shipment. The gateway should not react only to the phrase “stop shipment” or the agent’s risk score. It should determine whether the data comes from an allowed source, whether it is current, which batch is involved, who owns the decision, and whether automatic stoppage has been pre-authorized for that scope.
A threshold alone does not create a decision. Every threshold must be connected to the metric definition, measurement period, data quality, data freshness, product or process scope, consequence severity, and accountable owner. A number that is statistically notable does not necessarily have the authority to create operational disruption.
Rules should move away from vague language. Instead of writing, “If risk is high, inform the manager,” the rule should specify which variables determine risk, which role receives the notification, when a task is created, who may approve it, and after which decision a particular tool may be invoked.
Every rule needs, at minimum, an entry condition, validity scope, priority, permitted output, decision owner, expiration time, and audit-record requirement. Validity scope specifies the unit, process, data type, or consequence level to which the rule applies. Expiration time prevents the use of authorizations or rules that no longer match operational conditions.
Rule conflicts must be designed in advance rather than delegated to the model at runtime. A base rule can state that the more restrictive output takes precedence: deny or no-op overrides allow, and require-approval takes precedence over automatic execution. If that ordering does not resolve the conflict, the default output should be require-approval and the conflict reason should be recorded in the decision receipt.
Fail-safe behavior must also be explicit. If the policy gateway is unavailable, the data source cannot be validated, audit logging cannot be completed, or approval status cannot be verified, sensitive tools must not be allowed to execute. In that state, the system can return no-op or create-task and notify for human review, but it must not issue allow.
The same principle should apply to incomplete data. A missing case identifier, an unclear owner, stale data, a duplicate request, or insufficient evidence is not a reason for faster execution. The gateway should reject the request, create work to complete the information, or send it to a human approval path.
Notify and create-task are two different outputs. Notify creates awareness and does not create a new execution commitment. Create-task should include an owner, due date, status, and expected output. Blending the two either produces ineffective alerts or turns every low-value signal into a work queue.
Require-approval should not be merely a confirmation button. The approval request should show what action is intended, which evidence supports it, what scope it covers, what consequence it has, and how long it remains valid. The approver should be able to accept the action, reject it, narrow its scope, or return it for further evidence.
Allow is appropriate only for actions with limited impact scope that are reversible, or have a clear rollback path, and are governed by a stable, tested rule. Superficial similarity between two requests should not create identical authorization. A change in data source, impact scope, tool type, or action consequence should trigger authorization assessment again.
Decision logging is part of control, not additional administration. Each event should show which inputs were received, which policy version was applied, which rules matched, what conflict occurred, which output was issued, who approved it, and what result final execution produced. Without this receipt, improving rules and investigating errors becomes dependent on guesswork.
Evaluation of this architecture should not focus only on the quality of the agent’s responses. Boundary scenarios such as incomplete data, conflicting rules, duplicate requests, expired approvals, changed ownership, unavailable tools, and partially completed actions should also be tested. The important measure is whether the system moves to a safer state under ambiguity, not whether it merely produces more fluent output.
To begin, there is no need to put every process behind a policy gateway. Choose one frequent decision with a defined consequence; limit possible actions to the five outputs; define an owner, threshold, and expiration time for each output; and separate cases requiring approval from cases that may execute. Then refine the rules using decision receipts rather than expanding the agent’s authority with a larger prompt.
Maturity in using agents means that the organization knows exactly which signal becomes which action, under which conditions, and with which accountable owner. In this model, the agent increases the speed of observation and decision preparation, while independent policy defines the boundary of authority. This separation turns AI from an unpredictable trigger into a controllable component of operations.
اگر این موضوع شبیه مسئله واقعی کسبوکار توست، از چکاپ تصمیم شروع کن.
یک مسیر کوتاه برای روشنکردن مسئله، گلوگاه تصمیم و قدم بعدی؛ بدون فرم طولانی و بدون تعهد.