انسان در حلقه نیست؛ دروازه تصمیم است
تأیید انسانی در فرآیند هوشمند نباید یک دکمه مبهم در انتهای کار باشد؛ باید دروازهای طراحیشده با شواهد، مسئول مشخص، مسیر بازگشت و ادامه امن باشد.
فهرست مطالب
بعضی تیمها وقتی از هوش مصنوعی در عملیات حرف میزنند، خیلی زود به یک جمله آرامشبخش میرسند: «نگران نباشید، آخر کار یک نفر تأیید میکند.» این جمله در ظاهر مسئولانه است، اما اغلب فقط یک ابهام بزرگ را پنهان میکند. چه کسی تأیید میکند؟ دقیقاً چه چیزی را میبیند؟ حق دارد چه چیزی را تغییر دهد؟ اگر رد کرد، جریان کار از کجا ادامه پیدا میکند؟ و اگر هیچکس در زمان مناسب پاسخ نداد، چه اتفاقی میافتد؟
اگر جواب این سؤالها روشن نباشد، تأیید انسانی کنترل نیست؛ یک دکمه تزئینی است. دکمهای که یا همه برای عبور سریع از آن فشار میآورند، یا کار را در یک صف بیصاحب متوقف میکند. در هر دو حالت، سیستم هوشمند قابلاعتمادتر نشده است؛ فقط نقطه مبهمی به آن اضافه شده که هنگام خطا، همه میتوانند مسئولیت را به گردن دیگری بیندازند.
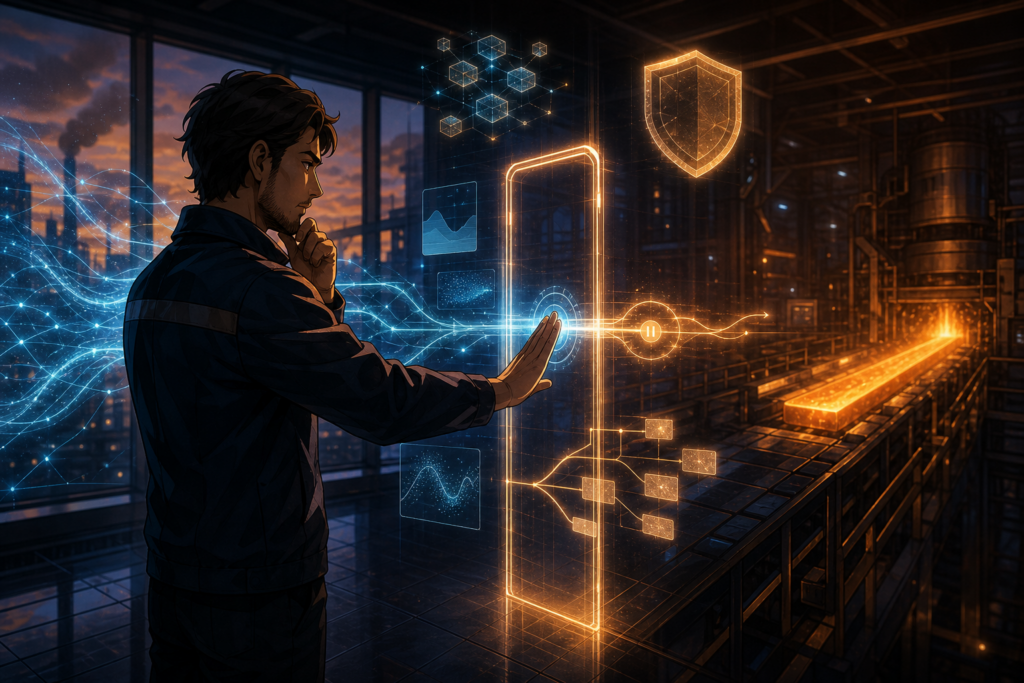
من ترجیح میدهم بهجای عبارت رایج «انسان در حلقه»، از «دروازه تصمیم» حرف بزنم. انسان قرار نیست دائماً کنار مدل بنشیند و خروجیهایش را تماشا کند. نقش انسان باید در لحظهای تعریف شود که تصمیم، هزینه، ریسک یا پیامدی واقعی دارد. این تفاوت کوچک در واژهها، تفاوت بزرگی در طراحی سیستم ایجاد میکند.
یک فرآیند هوشمند خوب از ابتدا همه کارها را برای تأیید انسانی نمیفرستد. چنین کاری فقط سرعت اتوماسیون را نابود میکند و آدمها را به اپراتور تأییدهای تکراری تبدیل میکند. از طرف دیگر، آزاد گذاشتن سیستم برای اجرای هر اقدامی هم نشانه بلوغ نیست؛ اغلب نشانه این است که هنوز هزینه خطا را جدی نگرفتهایم.
مسئله اصلی این است: برای هر اقدام، باید از قبل بدانیم در کدام یک از چهار وضعیت قرار دارد. آیا سیستم میتواند آن را خودکار انجام دهد؟ آیا فقط باید پیشنهاد بدهد؟ آیا باید پیش از اجرا تأیید بگیرد؟ یا اساساً نباید اجازه انجام آن را داشته باشد؟ این طبقهبندی باید بخشی از معماری باشد، نه تصمیمی لحظهای که بعد از دیدن خروجی مدل گرفته میشود.
مثلاً خلاصهکردن یک گزارش داخلی، دستهبندی اولیه درخواستها یا یافتن تناقض در چند فایل میتواند در بسیاری از شرایط خودکار باشد. اما تغییر رکورد عملیاتی، ارسال سفارش خرید، اصلاح برنامه تولید، ثبت نتیجه کنترل کیفیت یا صدور دستور مرتبط با تجهیزات، جنس دیگری از کار است. اینجا مسئله فقط درستبودن متن تولیدشده نیست؛ مسئله اثر آن تصمیم در دنیای واقعی است.
در محیط صنعتی این مرز حتی جدیتر میشود. یک سیستم ممکن است از دادههای حسگر، گزارش تعمیرات، سوابق کیفیت یا وضعیت موجودی به این نتیجه برسد که اقدامی لازم است. ارزش واقعی سیستم در این نیست که فقط هشدار بسازد؛ ارزش آن وقتی معلوم میشود که پیشنهاد را به اقدام قابلکنترل تبدیل کند: چه اقدامی، به چه دلیل، با چه سطحی از اطمینان، بر اساس کدام داده و با چه پیامد احتمالی.
دروازه تأیید باید درست پیش از همان نقطهای قرار بگیرد که اثر جانبی ایجاد میشود؛ نه خیلی زودتر، که تصمیمگیرنده با اطلاعات ناقص روبهرو شود، و نه خیلی دیرتر، که سیستم بخشی از عمل را انجام داده باشد و دیگر امکان بازگشت واقعی وجود نداشته باشد. اگر قرار است سفارش ثبت شود، تأیید باید پیش از ثبت باشد. اگر قرار است پارامتر عملیاتی تغییر کند، کنترل باید پیش از اعمال تغییر انجام شود، نه بعد از آنکه نتیجه نامطلوب دیده شد.
اما توقف جریان بهتنهایی کافی نیست. آدمی که باید تصمیم بگیرد، نباید با یک پیام مبهم مثل «تأیید میکنید؟» روبهرو شود. او به یک بسته شواهد نیاز دارد: پیشنهاد سیستم، دلیل پیشنهاد، دادههای اصلی پشت آن، محدودیتها و فرضها، سطح ریسک، گزینه جایگزین و نتیجه احتمالی هر انتخاب. تأیید خوب از انسان نمیخواهد حدس بزند؛ به او امکان میدهد قضاوت کند.
این بسته شواهد باید متناسب با نقش تصمیمگیرنده باشد. مدیر خرید لازم نیست جزئیات فنی همه دادهها را ببیند، اما باید بداند پیشنهاد چه اثری بر هزینه، زمان تحویل، موجودی و تعهدات دارد. مسئول کیفیت باید بتواند نمونهها، معیارهای رد یا قبول و موارد مغایر را ببیند. اپراتور یا مسئول نگهداری باید بداند کدام نشانهها به این پیشنهاد منتهی شدهاند و چه محدودیتهای ایمنی وجود دارد.
مالک تصمیم نیز باید روشن باشد. «تیم» تصمیم نمیگیرد؛ افراد مشخص، در نقشهای مشخص تصمیم میگیرند. وقتی یک درخواست برای تأیید فرستاده میشود، سیستم باید بداند مالک اصلی کیست، جایگزین او چه کسی است، مهلت پاسخ چقدر است و اگر پاسخی نرسید، مسیر ارجاع به مرحله بالاتر (escalation) به کجا میرود. فرستادن اعلان در یک گروه شلوغ، طراحی تأیید نیست؛ سپردن یک ریسک واقعی به شانس است.
همه تصمیمها هم دوگزینهای نیستند. تأیید یا رد، برای بسیاری از کارهای عملیاتی بیش از حد ساده است. دروازه خوب باید امکان اصلاح را هم فراهم کند. تصمیمگیرنده ممکن است با اصل پیشنهاد موافق باشد، اما مقدار، زمان، تأمینکننده، اولویت یا دامنه اجرا را تغییر دهد. اگر سیستم فقط دو دکمه دارد، انسان را مجبور میکند یا تصمیمی ناقص را تأیید کند یا کل جریان را بیدلیل متوقف سازد.
رد کردن نیز نباید پایان مبهم فرآیند باشد. سیستم باید بداند رد به چه معناست: لغو کامل، بازگشت برای جمعآوری داده بیشتر، ارجاع به فرد دیگری، ثبت بهعنوان استثنا یا درخواست تحلیل مجدد با محدودیت تازه. دلیل رد، اگر ثبت نشود، به یک فرصت یادگیری از دسترفته تبدیل میشود. اگر ثبت شود اما هیچوقت بررسی نشود، فقط انبار دیگری از داده ساختهایم.
نقطه مهم دیگر، وضعیت جریان (state) است. وقتی فرآیند برای تأیید متوقف میشود، باید بتواند بعداً دقیقاً از همان وضعیت ادامه پیدا کند؛ نه اینکه مدل دوباره از ابتدا مسئله را تحلیل کند و احتمالاً پیشنهاد متفاوتی بدهد. ورودیها، ابزارهای فراخوانیشده، خروجیهای میانی، سیاستهای فعال و شناسه تصمیم باید نگهداری شوند. این کار فقط یک جزئیات فنی نیست؛ شرط پاسخگویی است.
تصور کنید سیستم برای یک سفارش، قیمتها را جمع کرده، موجودی را بررسی کرده، محدودیت بودجه را دیده و پیشنهاد خود را ساخته است. اگر مدیر آن را با یک اصلاح تأیید کند، جریان باید همان پیشنهاد اصلاحشده را اجرا کند، نه اینکه بعد از تأیید، دوباره همهچیز را از نو تولید کند و یک تصمیم تازه بسازد. تأیید انسان باید به یک وضعیت مشخص متصل باشد، نه به یک گفتوگوی شناور و غیرقابلپیگیری.
هر تأیید خوب یک ردپا هم دارد؛ نه برای اینکه سازمان را با فرم و بوروکراسی خفه کنیم، بلکه برای اینکه بعداً بتوانیم بفهمیم چه شد. چه پیشنهادی مطرح شد، چه شواهدی در دسترس بود، چه کسی تصمیم گرفت، چه تغییری داد، نتیجه چه بود و آیا سیاستها درست عمل کردند؟ بدون این ردپا، ارزیابی سیستم به خاطره افراد و چند پیام پراکنده در ابزارهای مختلف وابسته میماند.
این ردپا به مرور کمک میکند سیاستها را بهتر کنیم. اگر یک نوع پیشنهاد تقریباً همیشه بدون تغییر تأیید میشود، شاید زمان آن رسیده که با کنترلهای مناسب به اجرای خودکار منتقل شود. اگر یک دسته درخواست دائماً رد میشود، احتمالاً داده، قاعده یا مدل مسئله دارد. اگر تصمیمها در یک نقطه بیش از حد معطل میمانند، شاید مالک اشتباه انتخاب شده یا بسته شواهد برای تصمیم کافی نیست. اینجا داده فقط برای مدل نیست؛ برای اصلاح فرآیند است.
برای شروع، لازم نیست یک معماری پیچیده و نمایشی بسازید. یک فرآیند مشخص را انتخاب کنید که هم ارزش عملیاتی دارد و هم اثر جانبی محدود و قابلکنترل. اقدامها را طبقهبندی کنید، سیاست توقف را بنویسید، برای تصمیمگیرنده بسته شواهد بسازید، مسیر تأیید، رد، اصلاح، عدم پاسخ و ارجاع به مرحله بالاتر را مشخص کنید، وضعیت جریان و ردپا را نگه دارید. بعد با نمونههای واقعی بررسی کنید که آیا انسان واقعاً میتواند تصمیم بهتری بگیرد یا فقط به مهر تأیید تبدیل شده است.
هوش مصنوعی وقتی مفید میشود که سرعت و دامنه تحلیل را بالا ببرد، نه اینکه مسئولیت را در مه پنهان کند. انسان در یک فرآیند هوشمند نباید نگهبان خستهای باشد که هر چند دقیقه یکبار دکمه تأیید را فشار میدهد. او باید صاحب یک دروازه تصمیم باشد: با اختیار روشن، شواهد کافی، حق اصلاح و رد، و سیستمی که بعد از تصمیم او امن، قابلپیگیری و قابلارزیابی ادامه میدهد.
اگر این دروازه را درست طراحی نکنیم، اتوماسیون فقط سریعتر اشتباه میکند یا سریعتر کار را پشت صف تأییدها پنهان میکند. اما اگر درست طراحی شود، میتوان بهتدریج بخشی از اعتماد را از افراد به فرآیند منتقل کرد؛ نه با حذف انسان، بلکه با قرار دادن او دقیقاً در جایی که قضاوتش ارزش واقعی دارد.
یک چکلیست ساده برای هر اقدام هوشمند این است: اثر واقعی این اقدام چیست؟ کدام سیاست اجازه آن را میدهد؟ چه کسی مالک تصمیم است؟ برای تصمیم چه شواهدی لازم است؟ آیا تأیید، رد و اصلاح هر سه ممکناند؟ اگر کسی پاسخ نداد چه میشود؟ سیستم از کدام وضعیت ادامه میدهد؟ و بعداً با چه ردپایی میتوانیم این تصمیم را بررسی کنیم؟ اگر برای این سؤالها جواب ندارید، هنوز این دروازه را طراحی نکردهاید؛ فقط یک دکمه گذاشتهاید.
در عمل، تفاوت میان یک دستیار نمایشی و یک سیستم قابلاستفاده، اغلب همینجاست. مدل شاید بتواند پیشنهاد خوبی بدهد، اما سازمان فقط زمانی میتواند به آن تکیه کند که بداند کجا باید متوقفش کند، چه چیزی را از او بخواهد، و بعد از تصمیم انسان چگونه بیدردسر و امن به کار برگردد.
این طراحی شاید هیجانانگیزترین بخش پروژه هوش مصنوعی نباشد. دموهای جذاب معمولاً درباره این بخش حرف نمیزنند. اما در کسبوکاری که با سفارش، موجودی، کیفیت، زمان، پول و ایمنی سروکار دارد، همین بخش تعیین میکند سیستم شما یک اسباببازی باهوش است یا یک همکار قابلاعتماد.
بهجای اینکه بپرسیم «کجا یک تأیید انسانی اضافه کنیم؟» سؤال دقیقتر این است: «کدام تصمیم باید از این دروازه عبور کند، با چه شواهدی، زیر نظر چه کسی و با چه راه بازگشتی؟» پاسخ به همین سؤال، فاصله میان اتوماسیون شلوغ و فرآیند هوشمند را مشخص میکند.
When some teams talk about AI in operations, they quickly reach a reassuring sentence: “Don’t worry, someone will approve it at the end.” It sounds responsible, but it often hides a large ambiguity. Who approves? What exactly do they see? What are they allowed to change? If they reject it, where does the workflow resume? And what happens if nobody responds in time?
If those answers are unclear, human approval is not a control; it is a decorative button. A button that people either click just to get through quickly, or one that leaves work stuck in an ownerless queue. In both cases, the intelligent system has not become more reliable. It has simply gained an ambiguous point where, when something goes wrong, everyone can shift responsibility elsewhere.
I prefer to speak of a “decision gate” rather than the common phrase “human in the loop.” A person is not supposed to sit beside the model all day and watch its outputs. The human role should be defined at the moment when a decision carries real cost, risk, or consequence. This small shift in wording creates a major shift in system design.
A good intelligent workflow does not send everything to a human for approval from the outset. That only destroys the speed of automation and turns people into operators of repetitive approvals. On the other hand, letting a system execute every action freely is not a sign of maturity either. It usually means the cost of error has not been taken seriously.
The central question is this: for every action, we should know in advance which of four states it belongs to. Can the system perform it automatically? Should it only make a recommendation? Must it obtain approval before execution? Or should it not be allowed to perform the action at all? This classification must be part of the architecture, not an improvised decision made after seeing a model output.
For example, summarizing an internal report, initially classifying requests, or finding inconsistencies across several files can be automated in many situations. But changing an operational record, issuing a purchase order, revising a production schedule, recording a quality-control result, or issuing an instruction related to equipment belongs to a different category. Here, the issue is not merely whether the generated text is correct; it is the real-world effect of the decision.
In industrial environments, this boundary becomes even more serious. A system may use sensor data, maintenance reports, quality records, or inventory status to conclude that an action is needed. Its real value is not in merely generating an alert. Its value becomes clear when it turns that recommendation into a controllable action: what action, for what reason, at what confidence level, based on which data, and with what possible consequence.
The approval gate should sit immediately before the point where a side effect is created. Not too early, when the decision-maker faces incomplete information; and not too late, when the system has already performed part of the action and genuine reversal is no longer possible. If an order is to be placed, approval must happen before placement. If an operating parameter is to change, control must happen before the change is applied, not after an undesirable result appears.
But pausing the workflow alone is not enough. The person who must decide should not face a vague message such as, “Do you approve?” They need an evidence package: the system’s recommendation, the reason behind it, the key supporting data, constraints and assumptions, the risk level, an alternative option, and the likely result of each choice. Good approval does not ask people to guess; it enables them to exercise judgment.
This evidence package should fit the decision-maker’s role. A procurement manager does not need to see every technical detail of the data, but they should know how the recommendation affects cost, delivery time, inventory, and commitments. A quality lead should be able to see samples, acceptance or rejection criteria, and nonconformities. An operator or maintenance lead should know which signals led to the proposed action and what safety constraints apply.
The decision owner must also be clear. A “team” does not make a decision; identifiable people in defined roles do. When an approval request is sent, the system must know who the primary owner is, who the backup is, how long the response window is, and where escalation goes if no response arrives. Sending a notification to a noisy group is not approval design; it is leaving real risk to chance.
Not every decision is binary either. Approval or rejection is too simple for many operational tasks. A good gate must also allow revision. The decision-maker may agree with the recommendation in principle but change the quantity, timing, supplier, priority, or scope of execution. If the system offers only two buttons, it forces the person either to approve an incomplete decision or to stop the entire workflow unnecessarily.
Rejection should not be the vague end of a process either. The system must know what rejection means: full cancellation, returning for more data collection, referring the case to another person, logging it as an exception, or requesting a new analysis under a new constraint. If the rejection reason is not recorded, it becomes a lost learning opportunity. If it is recorded but never reviewed, we have merely created another warehouse of data.
Another critical point is state. When a workflow pauses for approval, it must later resume from exactly that state, rather than having the model analyze the issue from scratch and possibly produce a different recommendation. Inputs, tool calls, intermediate outputs, active policies, and the decision identifier must be retained. This is not just a technical detail; it is a condition for accountability.
Imagine that a system has collected prices for an order, checked inventory, reviewed budget constraints, and produced a recommendation. If a manager approves it with one adjustment, the workflow should execute that adjusted recommendation. It should not regenerate everything after approval and create a new decision. Human approval must be attached to a specific state, not to a floating and untraceable conversation.
Every good approval also leaves a trail. Not to suffocate the organization with forms and bureaucracy, but so that later we can understand what happened. What recommendation was presented? What evidence was available? Who decided? What did they change? What was the result? Did the policies work as intended? Without that trail, evaluating the system depends on people’s memory and scattered messages across different tools.
Over time, this trail helps us improve policies. If one type of recommendation is almost always approved without changes, perhaps it is time to move it toward automated execution with appropriate controls. If a category of requests is repeatedly rejected, the problem may lie in the data, rule, or model. If decisions are consistently delayed at one point, perhaps the wrong owner was chosen or the evidence package is insufficient. Here, data is not only for the model; it is for improving the process.
To begin, you do not need to build a complex, theatrical architecture. Choose one specific process with operational value and limited, controllable side effects. Classify the actions. Write the stopping policy. Build an evidence package for the decision-maker. Define the paths for approval, rejection, revision, no response, and escalation. Retain state and the trail. Then review real cases to see whether the human can genuinely make a better decision or has merely become a rubber stamp.
AI becomes useful when it increases the speed and reach of analysis, not when it hides responsibility in fog. In an intelligent workflow, a human should not be a tired guard pressing an approval button every few minutes. They should own a decision gate: with clear authority, sufficient evidence, the right to revise and reject, and a system that continues safely, traceably, and evaluably after their decision.
If we do not design this gate properly, automation either makes mistakes faster or hides work faster behind approval queues. But if it is designed well, we can gradually transfer some trust from individuals to the process—not by removing people, but by placing them exactly where their judgment has real value.
A simple checklist for every intelligent action is this: What is the real-world effect of this action? Which policy permits it? Who owns the decision? What evidence is needed to decide? Are approval, rejection, and revision all possible? What happens if nobody responds? From which state does the system continue? And what trail will let us review this decision later? If you do not have answers to these questions, you have not designed approval yet; you have only added a button.
In practice, the difference between a showpiece assistant and a usable system often lies here. A model may be able to make a good recommendation. But an organization can rely on it only when it knows where to stop it, what to ask from it, and how to return to work smoothly and safely after a human decision.
This design may not be the most exciting part of an AI project. Attractive demos rarely talk about it. But in a business dealing with orders, inventory, quality, time, money, and safety, this is the part that determines whether your system is an intelligent toy or a dependable colleague.
Instead of asking, “Where should we add a human approval?” the more precise question is: “Which decision must pass through this gate, with what evidence, under whose authority, and with what path back?” The answer to that question defines the gap between noisy automation and an intelligent workflow.
اگر این موضوع شبیه مسئله واقعی کسبوکار توست، از چکاپ تصمیم شروع کن.
یک مسیر کوتاه برای روشنکردن مسئله، گلوگاه تصمیم و قدم بعدی؛ بدون فرم طولانی و بدون تعهد.